What WebAuthn Level 3 standardized
August’s Recommendation established a reference; credential storage and individual implementation still needed attention.
- Event / announcement date
- 2026-08-25
- Earliest linked source date
- 2024-10-11
- NewsTumble first published
- 2026-10-26T23:21:07Z
- NewsTumble updated
- 2026-10-26T23:21:07Z
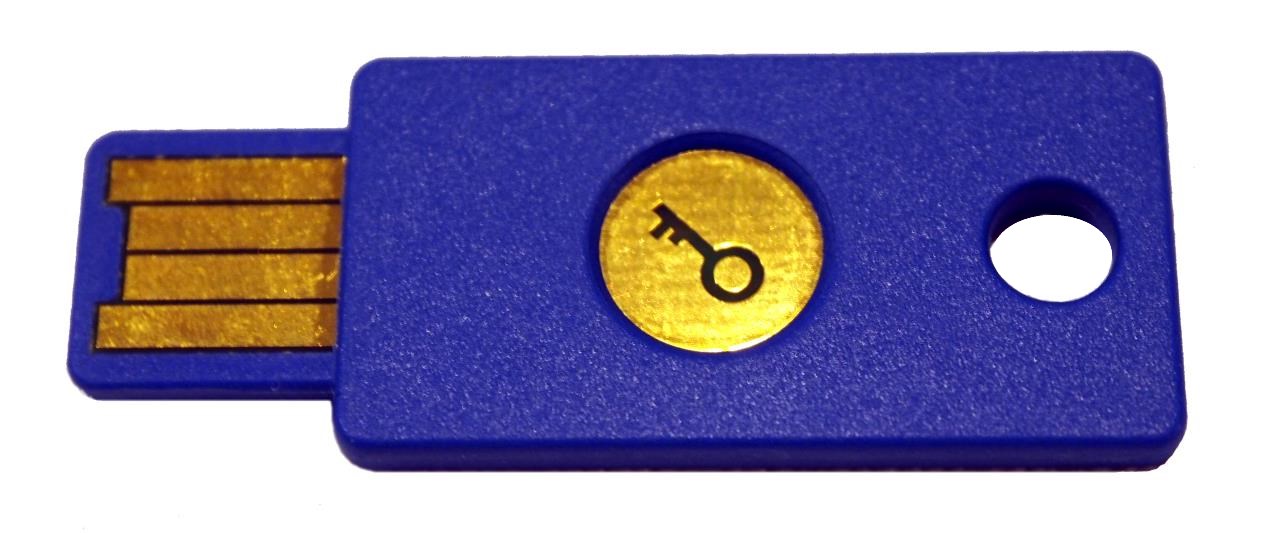
Historical report — W3C published Web Authentication Level 3 as a Recommendation on August 25, 2026. It describes public-key credentials scoped to a particular service, browser-mediated access to authenticators and requirements for user consent. The publication supplied a standard, rather than a test result for every implementing service. [1]
MDN’s protocol explanation separates registration from later authentication. A server sends a random challenge, and an authenticator returns a signature that can be verified with the registered public key. That supplies proof of possession without presenting the private key as the login secret. The site still needs an account-and-credential registration flow. [2]
Storage is another choice. FIDO’s explanation distinguishes passkeys synced across devices from credentials bound to one device, and describes local approval through a biometric, PIN or pattern. Those arrangements affect how the credential is available to its user. The same broad authentication framework can therefore support different portability and local-unlock arrangements. [3]
NIST’s guideline, finalized July 31, 2025, explains WebAuthn phishing resistance through verifier-name binding: the authenticated domain determines the secret selected. Manually entered codes lack binding to the specific session. That design distinction does not independently establish whether a particular service implements the standard correctly. [4]
The source
- W3C: Web Authentication: An API for accessing Public Key Credentials Level 3 is now a W3C Recommendation ↗
Source published 2026-08-25 · reviewed October 26, 2026 - MDN Web Docs: Web Authentication API ↗
Undated reference · reviewed October 26, 2026 · Publication date is not stated; last modified February 19, 2026. - FIDO Alliance: Passkeys ↗
Source published 2024-10-11 · reviewed October 26, 2026 · Page metadata records a September 16, 2026 modification. - NIST: Digital Identity Guidelines: Authentication and Authenticator Management ↗
Source published 2025-07-31 · reviewed October 26, 2026 · Final-release date from NIST’s publication record.
About this item: Retrospective report. No first-hand reporting or independent testing is claimed. Corrections policy.